Phishing Training: What the Evidence Shows
Key takeaways · 11 min read
- In one large study, about a third of employees clicked at least one test email over 15 months.
- Warning banners cut clicks sharply, while the most common kind of training page did not and may have backfired.
- Four large US and European studies since 2019 found little or no lasting training effect.
- Click rates depend mostly on how hard the test email is, so dashboards can mislead.
In this article
- Why phishing still works
- The largest test: 14,733 employees over 15 months
- Warnings worked. Training did not
- Three more large studies, one direction
- Where the good results came from
- What the click actually measures
- What lowered the risk instead
- What this means for you
- If you clicked: what to do and where to report
- Questions people ask
- The short version
- Sources
Most people who work in an office have had the email. It looks like a parcel notice, a password expiry warning or a shared document. You click, and instead of a login page you land on a cartoon fish and a short lesson: this was a test, and you failed it. Somewhere, a dashboard records the click.
Simulated phishing and the training that follows it are now a standard part of working life. Insurers ask about them, auditors check for them, and a whole industry sells them. The idea is simple and intuitive: people are the weak point, so teach them to spot the bait.
The evidence is less simple. Researchers have recently run the largest field studies yet, with tens of thousands of employees who did not know they were being studied. Several found that the most common kind of training changed almost nothing, and one found that it made some people more likely to click. This article covers what those studies measured, where the older positive results came from, and what actually lowered the risk.
Why phishing still works
Phishing is not a technical attack in the usual sense. It asks a person to do something: open a link, type a password, approve a payment or call a number. It works because the people receiving it are busy and a convincing message looks exactly like the hundred genuine ones that arrive every week.
Phishing remains the most reported form of online crime. The FBI’s Internet Crime Complaint Center listed phishing and spoofing as the largest complaint category in its 2024 report, with 193,407 complaints. That figure counts only the people who reported it, and most messages that fool someone are never reported at all.
One successful message can cost enormously. In September 2023, attackers who had found an employee’s details online phoned the IT help desk at MGM Resorts, posed as that employee and had the account reset. The resulting ransomware attack disrupted hotels and casinos in Las Vegas for days, and MGM told investors it expected a hit of about $100 million to one quarter’s earnings. No email link was involved, which is a reminder that phishing is a method of persuasion, not a file format.
The largest test: 14,733 employees over 15 months
In 2022, Daniele Lain, Kari Kostiainen and Srdjan Čapkun at ETH Zurich published a field experiment run with a large company in Europe. Between July 2019 and October 2020 the company sent each of 14,733 employees eight different simulated phishing emails, at random times. The employees knew the company might test them but did not know a study was running.
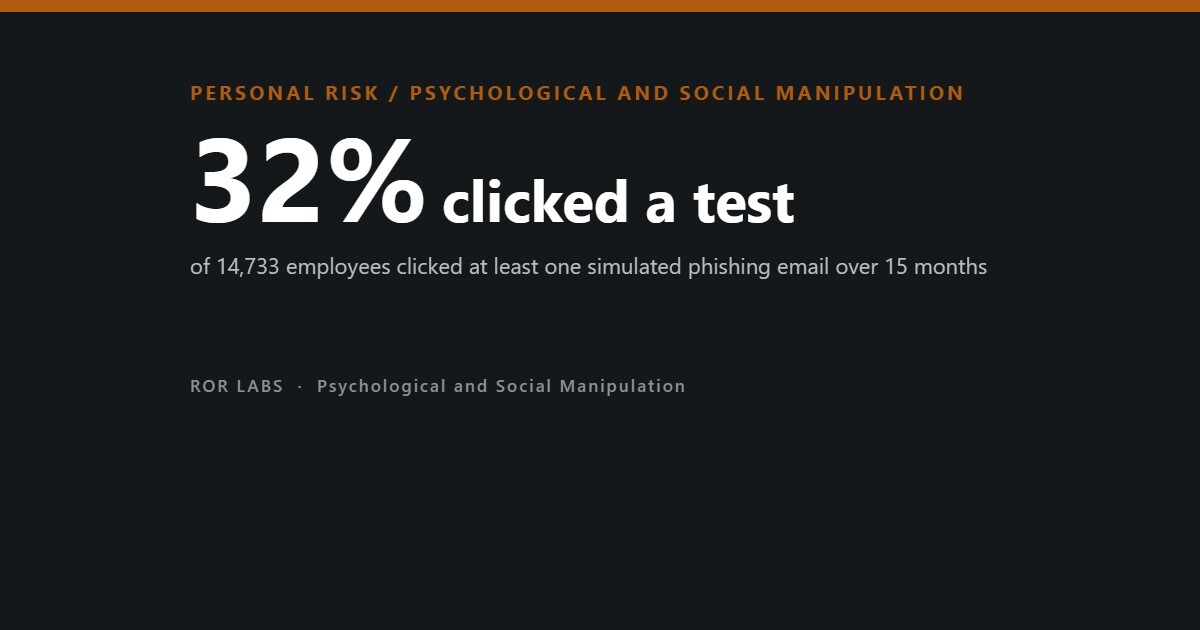
Of the 117,864 simulated emails sent over the whole period, 5.67% were clicked. That sounds low, but it added up: 32.1% of employees clicked at least one, and 25.4% went further and did something dangerous, such as entering their password or opening an attachment. Given enough attempts, a third of a well-run organisation took the bait at least once.
Simulated phishing at one European company, 2019–2020
Eight test emails sent to each of 14,733 employees at random times over 15 months.
Lain D, Kostiainen K, Čapkun S, IEEE Symposium on Security and Privacy, 2022. 25.4% of employees also took a dangerous action such as entering a password.
Warnings worked. Training did not
The study tested two common defences at the same time. Some employees saw a warning banner, either short or detailed, on top of suspicious emails, and others saw none. Separately, half of those who fell for a test email were sent to a training page explaining what they had missed, and half were not.
The warnings had a large effect. Employees without warnings clicked 3,964 times over the study, against 1,427 clicks with a short warning and 1,289 with a detailed one. The detailed version was no better than the short one.
The training went the other way. Employees shown the training page after a failure clicked more often afterwards, with 3,593 clicks against 3,087 in the group that saw no training page. Among people who fell for two or more tests, there were 801 in the training group and 647 without it.
Clicks on test emails by warning banner
Total clicks in each randomly assigned group over 15 months.
Lain D, Kostiainen K, Čapkun S, 2022. The difference between short and detailed warnings was not statistically significant.
The authors were careful about what this means. One specific and very common approach, a voluntary training page after a failed test, did not work in that company; that does not show all training is useless. In a follow-up questionnaire, 43% of those who remembered the page said it had made them feel safe, and 40% said the company was protecting them from bad emails. The researchers suggested a false sense of security as one possible explanation.
What happened after a training page
Employees who fell for a test email, with or without being sent to a training page.
| No training page | Training page | |
|---|---|---|
| Total clicks afterwards | 3,087 | 3,593 |
| Dangerous actions | 2,155 | 2,730 |
| Employees who fell for 2+ emails | 647 | 801 |
Lain D, Kostiainen K, Čapkun S, 2022. The training was voluntary and designed by a specialist company.
Three more large studies, one direction
A single study in one company could be a fluke. The next large tests came from the United States and pointed the same way.
William Gordon and colleagues reported on a hospital system in the Journal of the American Medical Informatics Association in 2019. Of 5,416 employees who received all 20 test campaigns, only 17.9% never clicked. The 772 who clicked five or more times were enrolled in mandatory training. Click rates fell over time for everyone, but the mandatory programme did not substantially change them, and the repeat clickers remained more likely to click.
In 2025, Grant Ho and colleagues at the University of California, San Diego, published an eight-month randomised trial with more than 19,500 employees of a large healthcare organisation. Completing the annual cybersecurity awareness course showed no significant link with failing a phishing test. For embedded training after a failure, the absolute difference in failure rates between trained and untrained staff was extremely small across every kind of content they tried. Most people spent very little time on the training page, and for some content, completing more training went with a higher chance of failing later tests.
Andrew Rozema and James Davis then repeated the question with 12,511 employees of a financial technology firm, in the proceedings of the ACM Web Conference in 2026. Neither interactive nor lecture-style training changed click rates or reporting rates in a statistically significant way. The difficulty of the email itself, rated with a scale developed by the US National Institute of Standards and Technology, did predict clicking.
Large field studies of phishing training
Employees who did not know they were in a study, receiving simulated emails at work.
| Study | People | Training tested | Effect on clicking |
|---|---|---|---|
| Gordon, US hospital, 2019 | 5,416 | Mandatory, for repeat clickers | No substantial change |
| Lain, European firm, 2022 | 14,733 | Voluntary page after a failure | More clicks |
| Ho, US health system, 2025 | 19,500+ | Annual course and embedded | Very small or none |
| Rozema, US fintech, 2026 | 12,511 | Interactive or lecture | Not significant |
| Baillon, Dutch ministry, 2019 | 10,000+ | Information or simulated experience | Fewer passwords given |
Gordon WJ et al, JAMIA, 2019; Lain D et al, IEEE S&P, 2022; Ho G et al, IEEE S&P, 2025; Rozema AT, Davis JC, ACM Web Conference, 2026; Baillon A et al, PLOS ONE, 2019.
Where the good results came from
Not every study is negative, and the reasons matter. Much of the early optimism came from the PhishGuru project at Carnegie Mellon University around 2008 to 2010. In a field test at a Portuguese company, Ponnurangam Kumaraguru and colleagues found that employees who received embedded training were significantly less likely to fall for a simulated attack one week later. Those studies were well designed but small, measured short intervals and were often run by the people who had built the training.
The strongest positive result comes from a large Dutch study. Aurélien Baillon and colleagues tested more than 10,000 employees of a government ministry and found that both a short information message and the experience of a simulated attack substantially reduced the share who gave away a password. Combining the two added nothing.
In Computers & Security, a 2024 scoping review by Nina Marshall, Daniel Sturman and Jaime Auton summed up 42 studies. It found good evidence of short-term improvement and very little evidence of lasting change in behaviour. People appear to get better at spotting phishing just after a reminder, and the effect fades.
What the click actually measures
A click may be a poor measure of skill, which could explain why the results disagree. Teodor Sommestad and Henrik Karlzén pooled 48 papers of field experiments in 2019 and found an average susceptibility rate of 21%, with the type of scam mattering enormously. Some kinds of message were orders of magnitude more successful than others.
The NIST scale study made the same point from the other side. Easy lures were clicked by 7.0% of employees and hard lures by 15.0%. A company that sends easier tests after a training course will see its click rate fall whether or not anyone learnt anything, and one that makes its tests harder will see it rise. The number on the dashboard often says more about the tests than about the people.
Click rate by how hard the email was
Simulated phishing emails rated on the NIST Phish Scale, 12,511 employees.
Rozema AT, Davis JC, Proceedings of the ACM Web Conference, 2026. Training type made no significant difference.
A 2024 follow-up by Lain and colleagues, at the ACM Conference on Computer and Communications Security, added a further clue. Employees improved after failing a test even when they did not read the training material, and being caught was as effective as the lesson itself. Interviews suggested that clicking had more to do with attention in a busy moment than with lack of knowledge.
What lowered the risk instead
The same 2022 study tested something that did help. The company added a button to its email program for reporting suspicious messages, and employees kept using it for the full 15 months without any sign of fatigue. On average, about 10% of reports of a test email arrived within 5 minutes of delivery and 30% to 40% within half an hour. The reports were right 68% of the time, and in the last five months the button helped find 252 real phishing campaigns aimed at the company.
That changes the question. A training programme asks every employee to be perfect every time. A reporting system needs only a few people to notice and speak up quickly, so that the security team can remove the email from everyone else’s inbox. Warning banners work in a similar way, interrupting the moment of inattention instead of trying to fix it in advance.
The biggest change is technical. Phishing mostly aims to steal a password or a one-time code, and security keys and passkeys are designed so that nothing a person types into a fake page would help an attacker. We looked at the evidence for them in our article on phishing-resistant sign-in.
What this means for you
If your employer runs phishing tests, failing one does not make you careless. Most people will click at least one test if they receive enough of them, and experts do too. A better response than shame is a habit: when a message asks you to act, especially urgently, stop and check through a route you already trust.
The same habit protects you at home. Scam texts about parcels, calls from someone claiming to be your bank and voice messages from a ‘relative’ in trouble all rely on the same pressure to act before thinking. Use the report button where there is one, turn on the strongest sign-in your accounts offer, and treat a request for a code or a password as a reason to hang up. We covered the voice version in our article on AI voice cloning scams.
If you clicked: what to do and where to report
The research above shows that a click is common and that blame helps little. This section is the order of actions in the FTC’s phishing guidance (last modified 11 October 2024) and CISA’s Secure Our World page.
Step 1: report the message. For email, forward it to the Anti-Phishing Working Group at reportphishing@apwg.org. For a text message, forward it to 7726 (SPAM). Then report it to the FTC at ReportFraud.ftc.gov. CISA adds that you can use the report option near the sender’s address or the “report spam” button in your email program instead of engaging with the message.
Step 2: if you clicked a link or opened an attachment. The FTC says to update your computer’s security software, run a scan and remove anything it flags.
Step 3: if you gave away personal or financial details. If you gave a scammer your Social Security number, a card number or a bank account number, the FTC points to IdentityTheft.gov for steps matched to what was exposed.
Step 4: make the next attempt harder. Both agencies recommend multi-factor authentication, which makes it harder for scammers to log in even with your username and password. CISA also recommends strong passwords with a password manager and prompt updates.
What we could not confirm. None of the official pages we read said to report to the impersonated company or to your workplace IT team, although that is common practice at many employers. Neither agency page said outright to change your password, though the post’s advice to do so after entering one on a fake page is standard. CISA’s small-business phishing page did not load, and we did not review FBI or IC3 phishing guidance.
What to do
Steps sorted by when they matter. Each one says how strong the evidence is: Measured Official advice Untested
Before
- Turn on the strongest sign-in your accounts offer. Untested see Sources
If it happens
- When a message asks you to act, especially urgently, stop and check through a route you already trust. Untested see Sources
- Treat a request for a code or a password as a reason to hang up. Untested see Sources
- Use the report button where there is one. Untested see Sources
What not to do
- Do not treat failing a phishing test as proof you are careless. Most people click at least one if they receive enough, experts included. Untested see Sources
Questions people ask
Does phishing training work?
Large field studies since 2019 have mostly found little or no lasting effect on click rates. Some smaller and earlier studies found short-term benefits.
Can phishing training make people worse?
In one study of 14,733 employees, those shown a voluntary training page after a failed test clicked more afterwards, possibly because it made them feel protected.
What reduces phishing clicks?
Warning banners on suspicious emails cut clicks by roughly two thirds in one large experiment. Reporting buttons and phishing-resistant sign-in also reduce harm.
How many people click on phishing emails?
An average of 21% across 48 field studies, but the rate depends heavily on how convincing the email is.
Is it my fault if I click?
Clicking is common and mostly about attention in a busy moment. Report it quickly; speed matters more than blame.
The short version
- In one large study, about a third of employees clicked at least one test email over 15 months.
- Warning banners cut clicks sharply, while the most common kind of training page did not and may have backfired.
- Four large US and European studies since 2019 found little or no lasting training effect.
- Click rates depend mostly on how hard the test email is, so dashboards can mislead.
- Reporting buttons, warnings and phishing-resistant sign-in do more than training alone.
This article summarises published research on workplace phishing training. It is not security advice for a specific organisation, and it does not suggest ignoring your employer’s policies. If you think you have entered a password or a code on a fake page, change the password and report it at once.
Further reading. Lain, Kostiainen and Čapkun, ‘Phishing in Organizations: Findings from a Large-Scale and Long-Term Study’, IEEE Symposium on Security and Privacy, 2022, is the key field study. Ho and colleagues, ‘Understanding the Efficacy of Phishing Training in Practice’, 2025, is the largest randomised trial.
Sources
- Lain D, Kostiainen K, Čapkun S. Phishing in organizations: findings from a large-scale and long-term study. 2022 IEEE Symposium on Security and Privacy, 842–859. doi:10.1109/SP46214.2022.9833766.
- Ho G, Mirian A, Luo E, and colleagues. Understanding the efficacy of phishing training in practice. 2025 IEEE Symposium on Security and Privacy, 37–54. doi:10.1109/SP61157.2025.00076.
- Gordon WJ, Wright A, Glynn RJ, and colleagues. Evaluation of a mandatory phishing training program for high-risk employees at a US healthcare system. Journal of the American Medical Informatics Association, 2019;26(6):547–552. doi:10.1093/jamia/ocz005.
- Rozema AT, Davis JC. Anti-phishing training (still) does not work. Proceedings of the ACM Web Conference 2026, 3147–3158. doi:10.1145/3774904.3792467.
- Baillon A, de Bruin J, Emirmahmutoglu A, and colleagues. Informing, simulating experience, or both: a field experiment on phishing risks. PLOS ONE, 2019;14(12):e0224216. doi:10.1371/journal.pone.0224216.
- Kumaraguru P, Sheng S, Acquisti A, and colleagues. Lessons from a real world evaluation of anti-phishing training. 2008 eCrime Researchers Summit, 1–12. doi:10.1109/ECRIME.2008.4696970.
- Marshall N, Sturman D, Auton JC. Exploring the evidence for email phishing training: a scoping review. Computers & Security, 2024;139:103695. doi:10.1016/j.cose.2023.103695.
- Sommestad T, Karlzén H. A meta-analysis of field experiments on phishing susceptibility. 2019 APWG Symposium on Electronic Crime Research, 1–14. doi:10.1109/eCrime47957.2019.9037502.
- Lain D, Jost TS, Matetić S, and colleagues. Content, nudges and incentives: a study on the effectiveness and perception of embedded phishing training. Proceedings of the 2024 ACM SIGSAC Conference on Computer and Communications Security, 4182–4196. doi:10.1145/3658644.3690348.
- Federal Bureau of Investigation, Internet Crime Complaint Center. Internet Crime Report 2024. 2025.
- MGM Resorts International. Form 8-K filed with the US Securities and Exchange Commission, 5 October 2023.
- FTC. “How To Recognize and Avoid Phishing Scams” (last modified 11 October 2024).
- CISA. “Recognize and Report Phishing” (Secure Our World, undated).