Four Points Identify You. That Is Why Your Location Is Worth Selling.
In This Series: Fraud & Digital Security
- Nobody Updates the Router. The FBI Says Criminals Are Living in the Old Ones.
- Your Voice Is No Longer Proof That It Is You
- A Credit Freeze Blocks the Rarer Kind of Identity Theft. Here Is What Blocks the Rest.
- The Two-Factor Code on Your Phone Will Not Stop This
- Changing Your Password Every 90 Days Made It Easier to Guess. The Standard That Started the Rule Now Says to Stop.
- They Asked 422 Burglars What Made Them Walk Away. The Locks Did Not Come First.
- Romance Scam Victims Were Better Educated Than People Who Never Fell for One. The Newest Version Never Asks for Money.
- The Same Offer Went From 11% Acceptance to 42%. Only the Buttons Changed.
Further reading: Means of Control — Byron Tau (Crown, 2024). A Wall Street Journal reporter’s investigation into location-data brokers and government surveillance purchasing — narrower than Zuboff’s argument, but more specific about how the data actually moves. Find it on Amazon (paid link)
Disclosure: this article contains affiliate links, marked (paid link). If you buy through one we may earn a commission, at no extra cost to you. As an Amazon Associate I earn from qualifying purchases. It costs you nothing and it does not change what we recommend.
Key takeaways · 14 min read
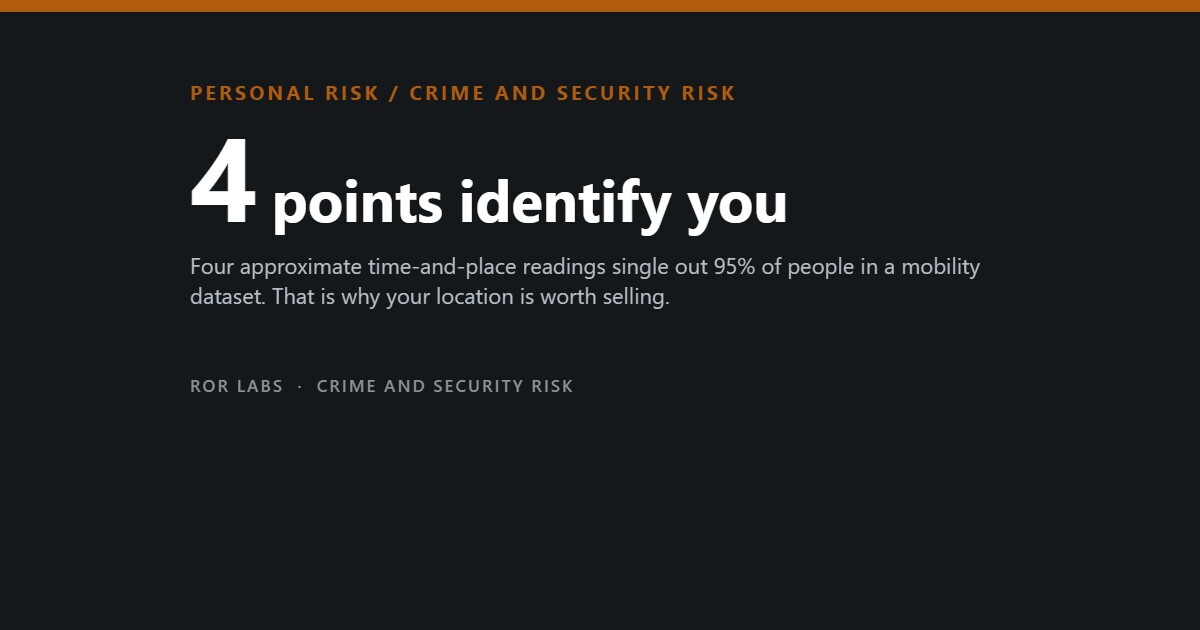
- Four known places-and-times identify 95% of people in an anonymised mobility dataset. “Anonymised” means the name was not attached, not that it cannot be.
- Coarsening the data barely helps: uniqueness decays as roughly the 1/10 power of resolution.
- The main pipe is real-time bidding. A bid request broadcasts your device ID and location to many bidders at once.
- Losing the auction does not lose the data. The FTC found a broker retaining what it received from auctions it never won.
On 1 August 2026, California switched on something that has never existed anywhere before: a single web form where a resident can tell every registered data broker at once to delete what they hold. It is called DROP, brokers have to check it at least every 45 days, and it went live three weeks ago to almost no coverage.
It exists because of a problem the industry spent a decade insisting was not one. The data being bought and sold is described as anonymous: no name attached, just an advertising identifier and a string of coordinates. The claim is that this makes it harmless. Research has said otherwise since 2013.
This article covers where that data actually comes from, which is stranger than most people expect and involves an auction you are entered into hundreds of times a day. It then turns to what regulators found when they finally looked inside two of these companies, and which of the available defences do anything. Unusually for this site, there is almost nothing here to sell you.
Four points are enough
The foundational study appeared in Scientific Reports in 2013, by de Montjoye, Hidalgo, Verleysen and Blondel. They took fifteen months of mobile phone mobility data for about 1.5 million people, stripped of names, with location recorded at the level of the cell antenna and time recorded to the hour, roughly the crudest useful resolution there is.
The question was how many known points about a person it takes to pick their trace out of the crowd.
Four spatio-temporal points identify 95% of people
Anonymised mobility traces, 1.5 million individuals, 15 months, hourly resolution at antenna level.
Source: de Montjoye, Y.-A., Hidalgo, C.A., Verleysen, M., Blondel, V.D. “Unique in the Crowd: The privacy bounds of human mobility.” Scientific Reports 3, 1376 (2013).
When a company says its location dataset is anonymised, the accurate translation is: we did not attach the name ourselves. Whether the name can be reattached is another matter, and usually the answer is yes, for anyone with a modest amount of outside information. The industry described below rests on exactly that gap.
The auction you are entered into all day
Most people assume location data leaks because an app they installed sells it. That happens, but the larger and less intuitive pipe is real-time bidding, the mechanism behind almost every advert you see in an app or on a web page.
When an app has an advertising slot to fill, it broadcasts a bid request to an exchange describing the opportunity so bidders can decide what it is worth: device identifier, app, and often precise location. The exchange forwards the request to many potential buyers simultaneously. One wins and shows an advert, but all of the others still received the data.
Losing the auction does not mean losing the data
The FTC found one broker harvesting from auctions it never won.
Source: Federal Trade Commission complaint against Mobilewalla, December 2024.
What regulators found when they looked
Two U.S. Federal Trade Commission cases opened this industry up, and they read best as descriptions of ordinary practice. Neither company was accused of a breach. Both were doing what the business does.
Two enforcement actions, two years apart
Both settled with orders restricting the sale of sensitive location data — the first of their kind.
| X-Mode Social / Outlogic (Jan 2024) | Mobilewalla (Dec 2024) | |
|---|---|---|
| How the data was gathered | Its own apps — including a nightlife app called Drunk Mode — plus a software kit embedded in other developers’ apps, plus purchases from other brokers | Real-time bidding exchanges and third-party aggregators, retaining data from auctions it did not win |
| Scale | Sold to hundreds of clients across real estate, finance and government contracting | More than 500 million unique advertising identifiers paired with precise location, January 2018 to June 2020 |
| What the data revealed | Visits to medical and reproductive health clinics, places of worship, domestic abuse shelters, LGBTQ+ locations and protests | Visits to pregnancy centres used to build a “pregnant women” segment; attendance at George Floyd protests, with inferred racial background and home city |
| What the order requires | Stop selling sensitive location data; delete what was collected; verify upstream consent; provide deletion and opt-out | No sale or use of location tied to military sites, churches, healthcare and correctional facilities, union offices, political gatherings or LGBTQ+ locations; no collecting auction data for other purposes; provide deletion |
Sources: Federal Trade Commission press releases and complaints, “FTC Order Prohibits Data Broker X-Mode Social and Outlogic from Selling Sensitive Location Data” (January 2024) and “FTC Takes Action Against Mobilewalla for Collecting and Selling Sensitive Location Data” (December 2024).
The FTC chair’s framing is the clearest short statement of why this matters: geolocation data can reveal not just where a person lives and whom they spend time with, but which medical treatments they seek and where they worship.
Why the “sensitive place” frame is too narrow
The orders above work by listing categories of place: clinics, churches, shelters, union offices. That is a sensible legal instrument but an incomplete model of the risk. Most of what a location trace reveals is a pattern rather than a single sensitive visit, and patterns are made of entirely ordinary places.
What an ordinary trace discloses without visiting anywhere sensitive
None of the inferences below require a protected location. All of them fall out of the pattern.
Sources: de Montjoye et al., Scientific Reports (2013); FTC complaints against Mobilewalla and X-Mode Social/Outlogic.
What actually helps, in order
Individual action is weaker here than in most subjects this site covers, because the collection is structural. That is no reason to do nothing, since the measures below genuinely reduce what is emitted, but anyone promising you disappearance is selling something.
Ranked by how much data each one stops
Every item on this list is free.
Sources: California Privacy Protection Agency, DROP; Federal Trade Commission consumer guidance; platform privacy settings documentation.
The California mechanism deserves a note of its own. It is genuinely new, and it is the first thing on this list that acts on data already collected rather than data yet to be emitted.
DROP: one request, every registered broker
California’s Delete Request and Opt-Out Platform, operated by the state privacy agency.
2026the date consumers could begin submitting deletion requests through a single verified form
daysthe maximum interval at which every registered data broker must check the platform and process the requests waiting there
Source: California Privacy Protection Agency, Delete Request and Opt-Out Platform (DROP) and Data Broker Registry; California Delete Act (SB 362), as amended by SB 361.
The shortest shopping list on this site (paid link)
There is very little here that a purchase fixes. One item earns its place, and not for the reason people buy it.
Browse on Amazon →
Three things we are deliberately not linking, and this is the section that matters.
VPNs marketed as location privacy. A VPN hides your IP address from websites. It does nothing whatsoever about GPS, and an app you granted location permission to reads the satellite fix directly — the tunnel is irrelevant. This is one of the most heavily advertised false claims in consumer technology and the affiliate commissions on it are large, which is presumably related.
Paid data-removal subscriptions. They send opt-out requests to brokers on your behalf, which is a real service badly matched to this particular problem: they reach the brokers that publish an opt-out and comply with it, and those are the ones you could have reached yourself. California residents now have DROP, which reaches every registered broker for nothing. Elsewhere the honest position is that these services buy convenience, not coverage, and they should be sold that way.
“Anti-tracking” phone cases and privacy gadgets. A camera cover is fine. A case that claims to stop tracking is either a signal blocker, in which case your phone is off and you knew that, or it is nothing.
What the official pages say about location data brokers
This section collects what the FTC, California’s privacy agency and the Justice Department say about location data sales, and what opt-outs exist. It describes allegations and orders as the pages describe them. It is general information, not legal advice.
| Source | What it says |
|---|---|
| FTC v. Kochava: 2022 complaint, May 4, 2026 proposed settlement | The 2022 page says the FTC alleged the data could reveal visits to clinics, places of worship, shelters and recovery centres, and that a complaint is not a finding of wrongdoing. The 2026 proposed order would bar selling sensitive location data without express consent and takes force only after court approval. The case page shows the status as pending. |
| FTC final orders: X-Mode/Outlogic (Apr. 2024), InMarket (May 2024), Gravy/Venntel and Mobilewalla (Jan. 2025) | The orders ban selling or using sensitive location data and require programmes to flag sensitive places. Some require deleting data collected earlier. These rest on FTC allegations as the pages state them, and the pages give no consumer opt-out steps, except that InMarket must offer a way to withdraw consent and request deletion in its apps. |
| FTC, How Websites and Apps Collect and Use Your Information (modified July 2, 2026) | Limit location in your phone settings, turn off app permissions you do not need or delete the app, and delete or reset your advertising identifier. It says this reduces targeting but does not stop all tracking. |
| California Privacy Protection Agency, DROP (undated) | Launched Jan. 1, 2026 for California residents; free; one request goes to 600+ registered data brokers. Brokers must start processing from Aug. 1, 2026, a request can take up to 90 days, and the page expects the first cycle to finish by Nov. 2026. It makes no promise of fewer scams or spam calls. |
| Justice Department, data security rule (published Jan. 8, 2025) | Restricts certain bulk transfers of sensitive data, including precise location, to countries of concern. It regulates transactions by businesses and is not an opt-out tool for consumers. |
| Apple and Google support pages (companies): Apple tracking, Apple Location Services, Android location | On iPhone, Settings > Privacy & Security lets you turn off app tracking requests and manage Location Services per app. On Android, location can be switched off or set to approximate per app. Menu paths vary by device and version. |
We could not confirm several points. No FTC page we read gives step-by-step opt-out instructions for data brokers. We could not confirm whether the court has entered the Kochava order, or that brokers are actually processing DROP deletions since Aug. 1, 2026. DROP covers California residents only, and we did not review other states’ laws. We found no CFPB page on this and could not confirm any CFPB role, and the Justice Department page does not describe any consumer effect. The Apple page we read does not cover Precise Location or Apple’s own ad settings.
What to do
Steps sorted by when they matter. Each one says how strong the evidence is: Measured Official advice Untested
Before
- Turn off the advertising ID in your phone settings. It is the key that links records together over time. Official advice see Sources
- Set location to “while using” and “approximate” app by app. Almost nothing needs background or precise location. Official advice see Sources
- Delete apps you do not use, especially ad-heavy games and utilities, and audit permissions twice a year. Official advice see Sources
- Use the legal routes: in California, one DROP deletion request reaches every registered broker. Several other states, the EU and the UK give a deletion right too. Official advice see Sources
What not to do
- Do not expect any setting to make you disappear. For a trip you do not want in a dataset, the only reliable answer is to leave the device behind. Untested see Sources
Questions people ask
Does turning off location services solve this?
It removes the precise fix, the most valuable part, but does not make you invisible. Your network operator knows which cell tower you are attached to as a condition of the phone working at all, and IP addresses carry coarse location. What you remove is the metre-accurate, timestamped trail that makes a dataset uniquely identifying, which is most of the value, so it is worth doing.
Is this legal?
Largely, in the United States. That is why the FTC actions were brought under unfairness and deception rules rather than a privacy statute: the theory was that consumers had not meaningfully consented, not that collection is banned. In the EU and UK, the GDPR treats precise location as personal data and much of this practice sits on far weaker legal ground, which is one reason the datasets and the enforcement look different there.
I am not in California. Is DROP useless to me?
Directly, yes, since it is a California resident right. Indirectly it may reach further, because compliance systems built for one large market tend to be applied more broadly, and because it is the first working template for the rest. Meanwhile a growing number of U.S. states, and the EU and UK, give you an enforceable deletion right you can exercise against a named broker yourself.
Should I worry about this more than about scams?
No, and we would rather say so. Measured in money lost this year, fraud is a far larger and more immediate risk than data brokerage; that is the subject of our pieces on credit freezes and voice-cloning scams. Location brokerage is slower and shaped differently: it rarely costs you a specific sum on a specific day, and it is much harder to undo once the data exists.
What about my children’s phones?
The same settings apply and matter more, because free games carry heavy advertising loads and a child’s trace covers a school, a home and a routine. Disable the advertising identifier on the device, set location permissions to “while using” and approximate, and pick a different app if one demands background precise location for no reason.
The short version
- Four known places-and-times identify 95% of people in an anonymised mobility dataset. “Anonymised” means the name was not attached, not that it cannot be.
- Coarsening the data barely helps: uniqueness decays as roughly the 1/10 power of resolution.
- The main pipe is real-time bidding. A bid request broadcasts your device ID and location to many bidders at once.
- Losing the auction does not lose the data. The FTC found a broker retaining what it received from auctions it never won.
- Mobilewalla held 500 million+ advertising identifiers paired with precise location, and built segments from visits to pregnancy centres and protests.
- X-Mode gathered through its own apps and a kit inside other developers’ apps, and sold to hundreds of clients including government contractors.
- The real disclosure is the pattern of home, work, who you are with and what changed, none of which requires a sensitive destination.
- Free and effective: disable the advertising ID, set location to while using and approximate, delete unused apps.
- California’s DROP opened on 1 August 2026; brokers must check it every 45 days.
- A VPN does nothing about GPS. Paid removal services buy convenience, not coverage.
This article describes data practices and consumer rights as of August 2026. It is not legal advice, privacy law differs sharply by country and state, and the rules here are changing faster than almost any other subject on this site — check the current position with your own regulator before relying on any of it.
On the links above: some are affiliate links, marked (paid link). If you buy through one we may earn a commission at no additional cost to you. As an Amazon Associate I earn from qualifying purchases. We link to product searches rather than specific items so that recommendations do not break as models change, and we say plainly when we are choosing not to link something. Full policy: Affiliate Disclosure.
Sources
- de Montjoye, Y.-A., Hidalgo, C.A., Verleysen, M., Blondel, V.D. “Unique in the Crowd: The privacy bounds of human mobility.” Scientific Reports 3, 1376 (2013). (1.5 million individuals over 15 months; four spatio-temporal points identify 95%; uniqueness decays as the 1/10 power of resolution.)
- Federal Trade Commission. “FTC Takes Action Against Mobilewalla for Collecting and Selling Sensitive Location Data,” December 2024, and the finalised order, January 2025. (500 million+ advertising identifiers with precise location, January 2018 to June 2020; retention of real-time bidding data from unsuccessful bids; pregnancy centre and protest segments.)
- Federal Trade Commission. “FTC Order Prohibits Data Broker X-Mode Social and Outlogic from Selling Sensitive Location Data,” January 2024, and the finalised order, April 2024.
- California Privacy Protection Agency. Delete Request and Opt-Out Platform (DROP) and Data Broker Registry. (Consumer requests from 1 August 2026; brokers must access the mechanism at least every 45 days; annual registration each January.)
- California Delete Act (SB 362, 2023), as amended by SB 361 (2025).
- Identity Theft Resource Center. 2025 Annual Data Breach Report.
- FTC: Kochava case; X-Mode; InMarket; Gravy; Mobilewalla; consumer advice. California DROP; DOJ rule.